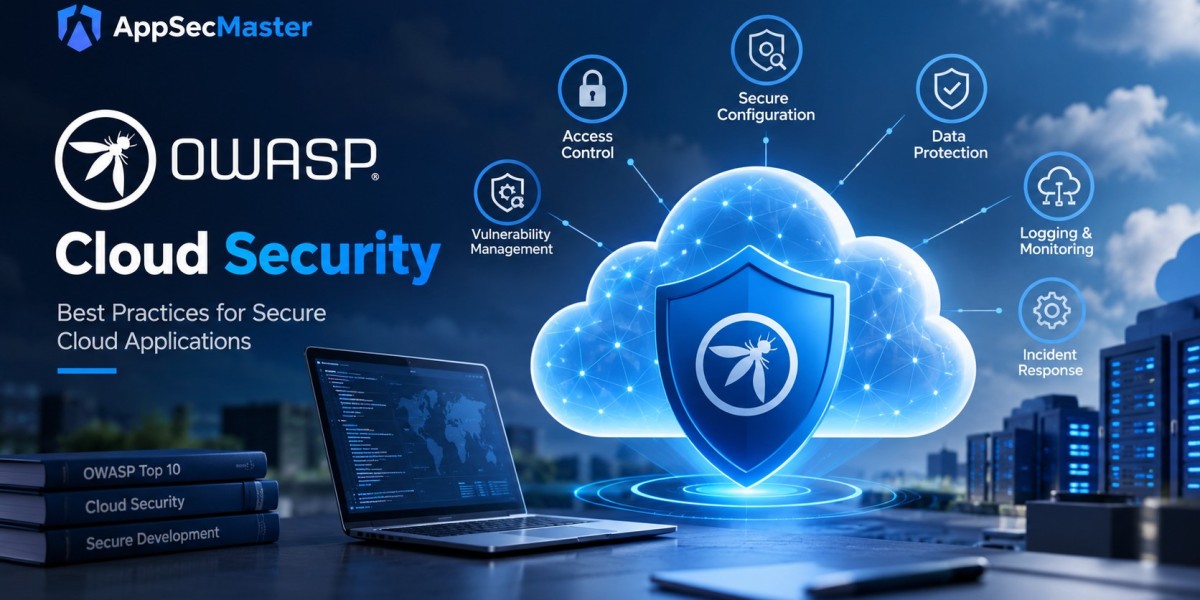

OWASP cloud security is the collection of free guidance, projects and risk lists from the Open Worldwide Application Security Project that help teams build and run cloud applications safely. Its best known resource is the CloudNative Application Security Top 10, which ranks the most common weaknesses in cloudhosted software, from insecure configuration to weak logging.
Moving an application to the cloud does not make it safer by default. It changes who owns which risks. The provider secures the data centers, hardware and core services, while your team secures everything it builds, configures and stores on top of them. Most cloud incidents trace back to the second half of that sentence: a storage bucket left open, a key committed to a repository, a role with far more permission than any task requires.OWASP cloud security guidance exists to make those failures easier to name, teach and prevent. This guide explains what the effort covers, how its risk lists work, what the biggest cloud security risks and vulnerabilities look like in practice and how to turn the guidance into daily habits. If you are new to the topic, start here and then follow the internal references into handson material.
What Is OWASP Cloud Security?
OWASP is a nonprofit community that publishes open, vendor neutral resources for application security. You probably know it for the OWASP Top 10, the awareness list that most security programs reference. Our breakdown of the OWASP Top 10 web application security risks shows how that list is organized and why it became a shared vocabulary for developers and auditors alike.OWASP cloud security is not a single product or certification. It is an umbrella for several community efforts that apply the same open approach to cloud environments. These include the OWASP Cloud Security project, which gathers guidance on securing cloud workloads and the OWASP CloudNative Application Security Top 10, a ranked list of the most important risks in modern cloud-native systems that use containers, orchestration, serverless functions and automated delivery pipelines.
Three traits make the material useful for beginners
It is open. Anyone can read, challenge and improve it, so it reflects realworld field experience rather than a single vendor's product roadmap.
It is vendor neutral. The principles apply whether you run on Amazon Web Services, Microsoft Azure, Google Cloud or a mix of all three.
It is risk focused. Instead of listing every control that exists, it ranks what goes wrong most often so you can prioritize.
Why Cloud Security Is Different From Traditional Application Security
Traditional application security assumed a fixed perimeter. You had servers in a known location, a firewall at the edge and a small number of people with administrative access. Cloud computing replaces that picture with something far more fluid.
Infrastructure is created by code and API calls, often hundreds of times per day. Identities, not network addresses, become the main security boundary. A single misconfigured policy can expose data to the entire internet within seconds. Meanwhile, teams ship faster, which means review time shrinks and the number of services involved grows.This is why cloud application security cannot be treated as a smaller version of network security. It sits across code, configuration, identity, pipelines and runtime behavior at the same time.If you work in a framework that restricts what code is allowed to do at runtime, a primer on code access security explains how permission models limit damage when code is compromised.
The OWASP CloudNative Application Security Top 10
The CloudNative Application Security Top 10 identifies ten risk areas that appear repeatedly in cloudnative environments. The exact wording of the project may evolve as it matures, but the themes are stable and worth learning. Our dedicated cloud security Top 10 breakdown goes deeper on each item; here is a plain language summary.
Insecure cloud, container or orchestration configuration. Default settings, open management consoles and permissive container options leave workloads exposed from day one.
Injection flaws. Untrusted input can reach databases, operating system commands and also cloud specific channels such as event messages and function triggers.
Improper authentication and authorization. Weak service to service authentication, missing checks on APIs and overbroad roles let attackers move between components.
CI/CD pipeline and software supply chain flaws. Compromised build systems, unsigned artifacts and poisoned dependencies deliver malicious code through trusted channels.
Insecure secrets storage. API keys, tokens and passwords stored in code, images or plain configuration files are easy to harvest.
Overpermissive or insecure network policies. Flat networks and unrestricted eastwest traffic allow one compromised container to reach everything else.
Using components with known vulnerabilities. Outdated libraries, base images and managed runtimes carry publicly documented flaws.
Improper assets management. Forgotten test environments, old API versions and unowned resources quietly expand the attack surface.
Inadequate compute resource quota limits. Without limits, a single abused workload can exhaust resources or run up enormous bills.
Ineffective logging and monitoring. If you cannot see data being exfiltrated or privileges being escalated, you cannot respond in time.
Read the list as a map of the application lifecycle. Items 1, 6 and 9 concern how things are configured, items 2, 3 and 7 concern how code behaves, items 4 and 5 concern delivery and secrets and items 8 and 10 concern visibility. A strong program needs coverage in every group. A disciplined secure code review guide helps reviewers look for the patterns that matter and language specific advice such as Java security code review turns generic principles into concrete things to check.
Cloud Security Risks and Vulnerabilities You Will Meet Most Often
Lists are helpful, but real incidents tend to follow a handful of repeating patterns. Learning these patterns is the fastest way to understand cloud data breaches.
Insecure Cloud Storage
Object storage is cheap, durable and easy to share, which makes it easy to share too widely. Public read access, overly generous access control lists and unauthenticated links have exposed customer records, backups and internal documents on many occasions. Modern platforms now ship guardrails such as accountwide public access blocks, but those controls only help if someone turns them on.
Exposed Cloud Credentials
Access keys leak through public repositories, build logs, mobile app packages, browser bundles and chat messages. Once an attacker holds a valid key, they do not need to exploit anything they simply call the provider's API as you. Automated scanners find leaked keys within minutes of publication, so rotation and short lived credentials matter more than clever hiding places.
Excessive Cloud Permissions
Teams under deadline pressure often attach wildcard permissions "just to make it work" and never revisit them. The result is an identity that could read every database, delete every backup or create new administrators. When that identity is compromised, the blast radius is the entire account. Related application layer flaws such as insecure direct object references let one user reach another user's data; you can practice that class of bug in the IDOR and broken access control lab.
Misconfigured Cloud Services
Managed databases reachable from the internet, debug endpoints left enabled, permissive crossorigin settings, unencrypted volumes and disabled audit logs all fall into this group. None of them require a sophisticated exploit. They simply require someone to look.
Cloud Data Breaches
Large cloud data breaches rarely start with advanced malware. They usually chain two or three of the weaknesses above: an exposed service, a leaked credential and a role that allows broad data access. Understanding the chain is more valuable than memorizing any one incident.
Cloud Security Best Practices to Start With
If you only have a week to improve your posture, focus on the following steps. They address the most frequent causes of incidents and map directly to the OWASP themes.
Enforce least privilege. Start every role with zero permissions and add only what a task needs. Review unused permissions on a schedule.
Turn on multifactor authentication for every human account and prefer short lived tokens over long lived keys for workloads.
Block public storage by default at the account or organization level and require an approved exception for anything public.
Centralize secrets. Remove credentials from code, images and environment files and load them from a managed secrets service at runtime.
Encrypt data at rest and in transit and manage keys separately from the data they protect.
Enable audit logging everywhere and send logs to an account that workload administrators cannot modify.
Scan infrastructure definitions before deployment so insecure settings are caught in review rather than production.
Patch dependencies and base images on a regular cadence and track an inventory of what you run.
Set quotas and budgets so abuse or runaway automation is detected and capped.
Rehearse incident response for the specific case of a leaked key or exposed bucket.
None of these require expensive tooling. They require ownership and routine.
Where Code Quality Meets Cloud Security
Cloud security is not only a configuration problem. The application code running in your functions and containers is just as exposed. Input handling, authorization checks, error messages and dependency choices all decide whether an attacker can turn a small mistake into a major incident.
That is why cloud programs should reuse proven coding standards. The OWASP secure coding practices give a checklist covering validation, authentication, session handling and error management that applies equally to cloudhosted services. Review is the second half of the equation. To keep up with delivery speed, many teams add automated code review to every pull request and some now evaluate the best AI code review tools to catch issues earlier. Automation finds the repeatable mistakes; humans still need to judge business logic and authorization design.
A Simple Mental Model
When you meet a new cloud risk, ask three questions: who is allowed to do this, what exactly can they reach and how would we know if someone abused it? Identity, exposure and visibility cover nearly every item in the OWASP list and the habit of asking them will serve you on any provider.
Learning by Doing
Reading about misconfiguration is useful, but skills stick when you exploit and fix real flaws. Handson practice in a safe environment lets you see how an injection payload travels, how a broken access check exposes records and how a small oversight becomes a full compromise. The web application hacking labs give you realistic targets and the web security CTF challenges add a competitive, puzzlestyle format that rewards persistence.A sensible learning path looks like this understand the shared responsibility model, learn the ten risk areas, practice the web vulnerabilities that underlie them, then repeat the same exercises against a small cloud account you own. Always test only systems you are authorized to assess and follow your provider's rules for security testing.
Conclusion
OWASP cloud security gives beginners a clear starting point in a field that can feel overwhelming. The shared responsibility model tells you what you own, the CloudNative Application Security Top 10 tells you what usually breaks and a short list of best practices tells you what to do first. Focus on identity, secrets, configuration, logging and code quality and you will close the gaps behind most realworld cloud data breaches.Security is a habit, not a onetime project. Pick one improvement from this guide, apply it this week and then practice the matching attack in a lab so you understand exactly what you are defending against. You can explore the full catalog of training on the AppSecMaster home page.
Frequently Asked Questions (FAQs)
What is OWASP cloud security?
OWASP cloud security refers to the free, community driven guidance and projects that help organizations secure cloud applications. It includes the OWASP Cloud Security project and the CloudNative Application Security Top 10, which ranks the most common risks such as insecure configuration, weak authentication, exposed secrets and poor monitoring.
Is the OWASP CloudNative Application Security Top 10 the same as the OWASP Top 10?
No. The classic OWASP Top 10 focuses on web application risks like injection and broken access control. The CloudNative Application Security Top 10 focuses on risks unique to cloud native systems, including container configuration, orchestration, pipelines, secrets storage and resource limits. The two lists complement each other and most cloud applications are affected by both.
What are the most common cloud security risks and vulnerabilities?
The most frequent problems are insecure cloud storage, exposed credentials, excessive permissions and misconfigured services. Attackers typically chain several of these together, for example by finding a leaked key and using an overprivileged role to reach sensitive data.
Do OWASP recommendations apply to AWS, Azure and Google Cloud?
Yes. The guidance is vendorneutral, so the same principles of least privilege, central secrets management, logging and configuration scanning apply on every platform. Only the names of the individual services differ.
How can a beginner start learning cloud security?
Begin with the shared responsibility model and the ten OWASP cloud native risk areas, then practice related web vulnerabilities in hands on labs and capture the flag challenges. Finally, apply the best practices to a small cloud account you control, using budgets and alerts to stay safe.